Jeisan
The name my working agents carry: an always-on server agent, a git author, a pod manager
- Role
- Operator and architect; Codex and Claude agents built the migration and the control plane
- Status
- In progress
- Source
- Private repository
- Stack
- Hermes Agent (NousResearch)OpenClawCodexPythonsystemdTelegramCloudflare WorkersGitHub ActionsTailscaleLinux
In numbers
52
skill packages carried over in the move to Hermes Agent
4
schedules restored after the move
5
least-privilege hops between Jeisan and a trading pod, ending at a strict server-side parser
15/ 15
same-host isolation checks passed before the worker plane went live again
1,117
tests passed, 90 skipped, when Claude-built changes were merged together in a disposable worktree before reaching main
The problem
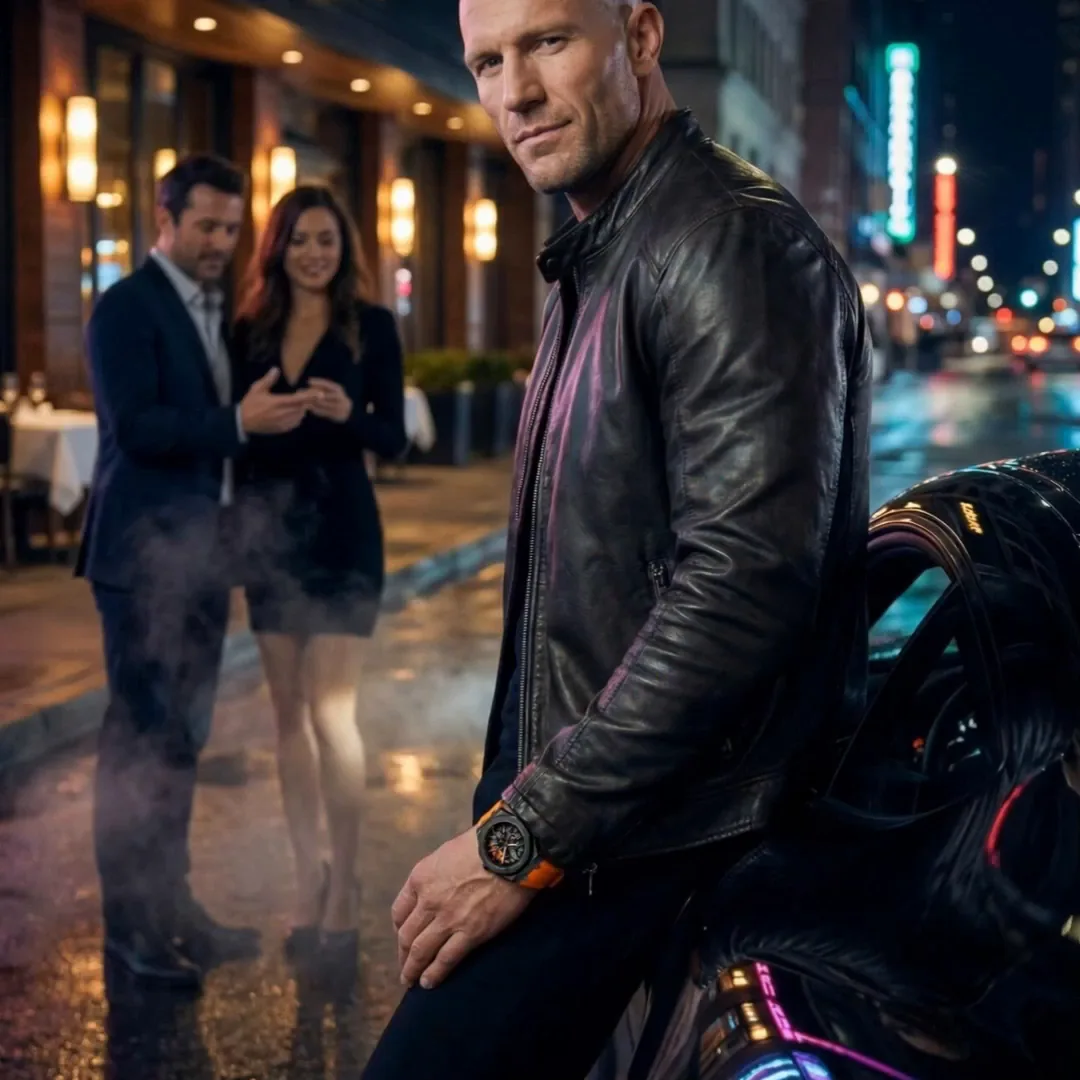
An agent that works while I am asleep needs a process that stays up, a memory that outlives the chat, credentials of its own, and limits it cannot talk its way past. Jeisan began as a character in one of the ValoxVSL ads, a tough-guy action hero. The name first went onto an OpenClaw workspace on a small cloud server: an identity file, memory, a lead tracker and scripts. Later the subscription it had run on no longer allowed that use, and I wanted it on my Codex subscription with nothing lost.
The approach
The name, the operating manual and the memory stay; the framework underneath can change. I gave Codex the move to NousResearch's open-source Hermes Agent and told it to run autonomously. One lead thread and its sub-agents did the work, and the same lead went on to build the control plane through which Jeisan manages the trading pods. Claude agents built parts of that control plane, and Codex reviewed them as a handoff from another author instead of trusting their completion reports.
How it works
One name, several jobs
The Hermes gateway on the server answers on Telegram and runs the schedules. The Discord account of my voice bridge is Jeisan Steisan. The same name is a git author: it wrote a link shortener on Cloudflare Workers end to end, including the CI workflow, the licence and the security policy. And it is the manager of the trading pods. Each job runs with its own credentials.
A persona for tone, hooks for the rules
The original persona file, written in the OpenClaw era, opens with "The actual rules. Not suggestions." It sets the goal of being useful before anyone asks, splits the work as "Georgi handles diplomacy. I handle tracking and preparation.", and puts the philosophy in one line: "Build assets, not jobs." The persona carries the character. The rules that matter are hooks, not prompts: in my setup PreToolUse guard hooks refuse a destructive command before it runs, defaults fail closed, and a secrets guard once blocked an agent's push to the trading repo because 64-character hex constants looked like keys. The agent did not force past it; it cleaned up and filed an issue.
A move that lost nothing
The migration followed Hermes' own OpenClaw workflow, with a preview and a restore point. It hit an upstream edge case, a workspace outside the OpenClaw home directory that made the archive step abort, and got through it with a reversible path workaround. A parity audit then checked 52 skill packages, the channel allowlists and four schedules against the old workspace. Migrated credentials that were already invalid were removed instead of ported, and stale memory was rebuilt from curated files, because the raw chat export held third-party data and credentials. The 99 KB result was scanned clean before it went in.
Credentials kept apart from execution
The desktop Codex refresh token was not copied: a single-use grant would have made Hermes and the desktop app compete for it, so the agent got its own OAuth grant. Workers receive access-only credentials and the refresh token stays in one central store. On the server, Jeisan's repository access is two units: an unprivileged executor, and a credentialed network unit that talks to one fixed origin. The agent runs the pinned stable release, v0.19.0, and my clone of Hermes carries no local commits.
A manager with a bounded mandate
Jeisan reaches the pods through a chain of least-privilege hops: a wrapper, an exact no-argument sudo rule, a root-owned key with a pinned host key, an SSH account with a forced command, and a strict server-side parser. It can observe and advise. The only production change is made by a root systemd timer with no model in it, and a live start would need an expiring, non-replayable mandate, root-attested config hashes and fresh signed exchange evidence. The policy and the mandate ship disabled. Independent watch jobs keep a sticky HALT that overrides the manager.
Deploys and reviews that distrust green
Adversarial reviews found fail-open bugs behind green unit tests: a forged advisor result, candidate code forging a test-completion marker, a kill window that stranded installer recovery. Each was fixed before deploy. Installs are transactional with rollback, the live checkout moves only after SHA-bound Linux CI evidence exists, and all 15 same-host isolation checks must pass. A nightly researcher, engineer and independent-reviewer graph works on the code and cannot merge, deploy or touch orders. When a Claude agent delivered five governance PRs, Codex merged them in a disposable worktree and ran the combined suite, 1,117 passed and 90 skipped, before any of them reached main.
What I chose, and what lost
Chose
A separate OAuth grant for the agent
Over
Copying the desktop refresh token to the server
A single-use grant would make Hermes and the desktop client compete for it.
Chose
The pinned stable release of Hermes Agent
Over
Tracking the upstream main branch
The local checkout turned out to be a snapshot whose local patch was already upstream. A pinned release is a known state the audit can be run against.
Chose
A signed, expiring mandate executed by a timer with no model in it, shipped disabled
Over
A confirmation on every trade, or an agent with open authority over the pods
I did not want to confirm each trade, and Codex, building it, would not give a language model open authority over money. The mandate states the envelope in advance, a timer carries it out, and a file can end it.
Outcome
The Hermes gateway came up with Telegram connected and is still running. The control plane is on main and ships disarmed: Jeisan observes and advises, and arming a pod stays a typed human decision. Hermes Agent is NousResearch's code; my part is the migration, the credential layout, the control plane and the rules around them. Unfinished: an allocator that would divide capital across the pods exists as a shadow-only core with no production input and no path to authority.
What comes next
Connect the shadow allocator to real inputs and score its proposals for long enough to judge them, before any authority path is written.
Gallery
Jeisan, as he first appeared in a ValoxVSL ad.
Jeisan, as he first appeared in a ValoxVSL ad.